See.
Lives inPortal
Client Vision turns every cloud account, finding and framework into one security posture your board can read, tracks every fix to closure, and publishes the proof your customers ask for. Run it yourself, or run it with 3HUE.
Screens show the Big Venture Incorporated demo workspace. All figures are sample data. Client Vision is powered by the AiVRIC platform.
Figures from the Big Venture Incorporated demo workspace, scan of Sep 19, 2026.
The glossary
Security programs are run in a handful of verbs. Client Vision gives each one a home, and every home reads from the same numbers.
Continuous compliance
Controls are cross-walked once. Each scan updates the pass rate for every framework you answer to, so the compliance dashboard your auditor sees and the posture score your board sees never disagree.
Two ways to run it
Self-serve
Managed by 3HUE
Both lanes run in the same workspace, with every decision audited on both sides. Compare the lanes and see pricing →
Sample reports · demo data
Three documents from the Big Venture Incorporated demo workspace: what the Snapshot hands leadership, what a board receives each quarter, and what the POA&M export looks like. Nothing to fill in; every figure is sample data.
 Snapshot readout
AI & Security Risk Posture Snapshot
What leadership receives on day ten: the posture score, the findings that matter, the AI governance read and the sequenced 90-day plan.
 Quarterly board pack
Security posture, quarter in review
The GROC briefing a Managed by 3HUE client’s board sees each quarter: one score, the risks that moved, the decisions the board owns.
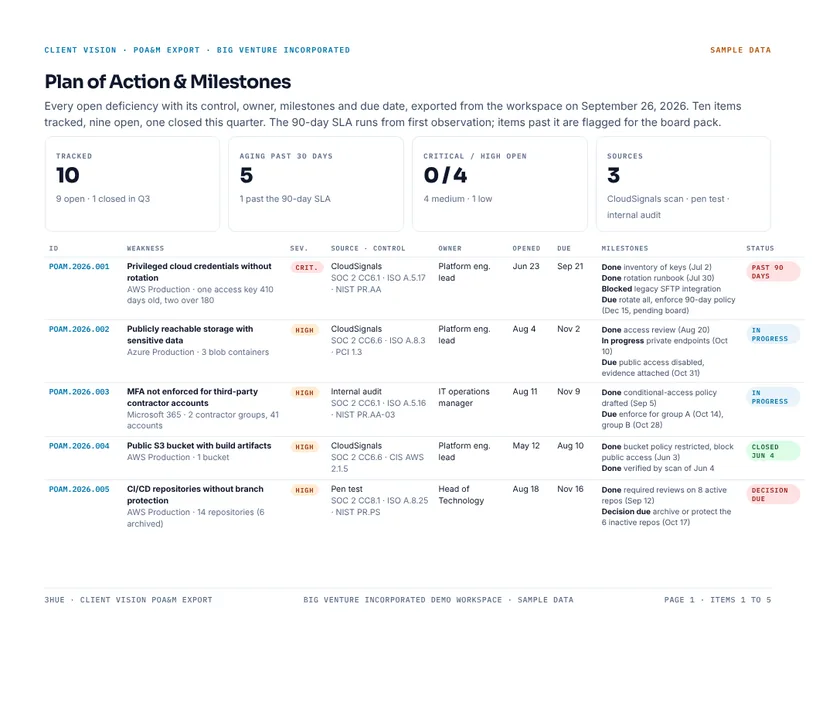 POA&M export
Plan of Action & Milestones
Every open deficiency with its control, owner, milestones and due date, exported from Client Vision the way an auditor or assessor receives it.
Side by side · read October 21, 2026
Vanta, Drata and Secureframe are good at what they were built for: collecting evidence from hundreds of integrations and getting a company through its audit. Client Vision was built for what comes after the audit: one posture score, every finding carried to closure, a board that gets a real read, and a named vCISO when you want the program run for you. The comparison is on those grounds, and every statement about another tool comes from that vendor’s own public pages, listed below.
Where those tools lead
Integration breadth and audit marketplaces. Vanta cites 400+ integrations and 35+ frameworks, Drata over 300 integrated tools and a network of 175+ audit firms, Secureframe 300+ integrations and a team of 30 in-house compliance experts. If the job is collecting HR, identity and SaaS evidence across hundreds of tools for one audit, those catalogs are larger than Client Vision’s CloudSignals connectors, and nothing here stops a company keeping one of them for evidence while Client Vision carries the posture score, the POA&M and the board pack.
How to read this
Prices are not compared here; Client Vision plans and the Snapshot fee are on the Pricing page, and none of the three vendors publishes a full price list. Vendor statements were read from the pages below on October 21, 2026 and are re-checked each quarter; if one has changed, tell us and it will be corrected. Vanta, Drata and Secureframe are trademarks of their respective owners.
Connected data sources
Scan findings, resources and risk treatments from your cloud estate. The system of record that decisions write back to.
AI use, model and governance signals, reported alongside the cyber estate.
Spend signals that turn remediation into opportunities, like committing compute to savings plans.
Questions
Client Vision is 3HUE's GRC software and the workspace behind 3HUE GRC Acceleration: it brings your cloud findings, risk register, POA&M, control baseline, decisions, threat intelligence and trust center into one place, and reports them through ROAR and GROC. Client Vision is powered by the AiVRIC platform.
The way 3HUE delivers governance, risk and compliance: the AI & Security Risk Posture Snapshot to establish where you stand, Client Vision to carry the program, and a named vCISO when you want 3HUE to run it with you. Readiness programs for SOC 2, HIPAA, CMMC and the EU AI Act all run in the same workspace.
It is a severity-weighted pass ratio across every check in a scan, graded out of 100. The demo workspace scores 71, a B−, across 2,835 checks. One formula feeds every view, so the Portal, ROAR and GROC always agree.
A Plan of Action and Milestones is the official record of pending remediation. Client Vision de-duplicates scan-derived and manual findings into one master per deficiency, gives each an owner, and flags anything open past 90 days.
ROAR is the Risk and Opportunities Assessment Report. Each scan produces an executive summary, top risks scored likelihood × impact, top opportunities, a remediation roadmap and trends, ready to freeze as a snapshot for the board.
No. TrustSignals publishes an approved snapshot of bands and coverage — security, compliance, privacy, resilience and AI governance — never raw findings. Documents stay in your own SharePoint, Drive or URL.
The demo workspace reports PCI DSS 4.0, NIST CSF 2.0, SOC 2, CIS Azure 3.0, NIS2, ISO 27001:2022, GDPR and CIS AWS 2.0 from the same scan.
Both. Run the workspace with your own team, or have 3HUE's practitioners run the program with you in the same workspace, with every decision audited on both sides.
Book a live walkthrough of Client Vision on a demo workspace. Fifteen minutes, your questions, real screens.